How we protect your invoice data
The concrete technical and organizational controls behind the Service, written in plain language. Every claim on this page maps to production code or a named sub-processor.
See the controls and their current limits.
Retention windows, role-based access with eight roles, and a full audit trail of every significant action. Procurement and compliance reviews can verify each one inside a trial workspace.
Inspect the evidence.
Product captures · sample workspace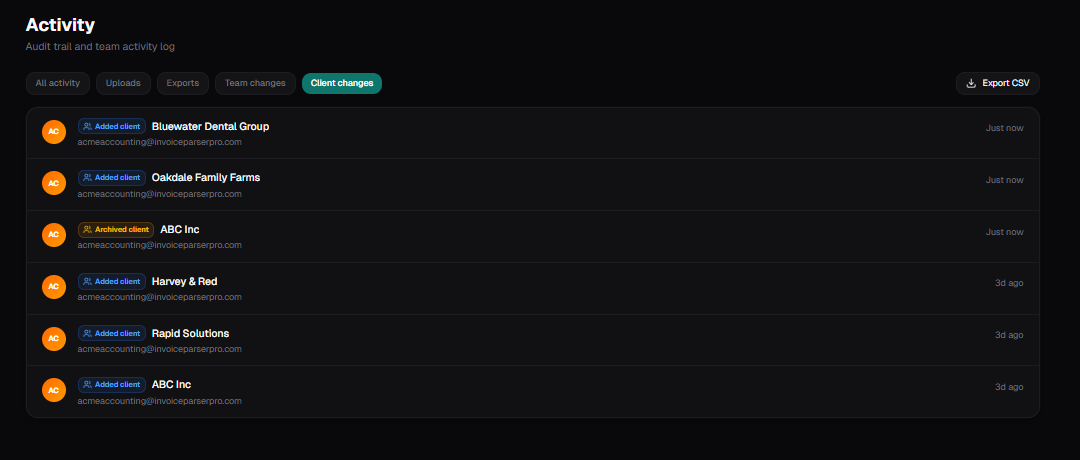
Look at the timestamp, actor and action together. This sample product capture shows recorded activity, not a live customer feed.
Evidence added to the product library . Select the image to read the original detail.
These are historical captures, not live monitoring. Verify current controls in your trial workspace.
Transport Security
All connections use enforced HTTPS/TLS. No unencrypted connections are accepted at any endpoint.
Credential Storage
Passwords are hashed with bcrypt. API keys, password-reset tokens and two-factor recovery codes are stored only as hashes. Two-factor secrets, client upload-link tokens and accounting connection tokens (QuickBooks Online, Xero, Zoho Books) are encrypted at rest using Fernet symmetric encryption with a server-held key.
Data Isolation
Each workspace's invoice data is scoped at the query layer: every request for workspace data is checked against the signed-in user's membership, and queries are filtered to that workspace. Files are stored per-workspace in Cloudflare R2 (US region) and extracted data is scoped per-workspace in our Postgres database. Stored files are encrypted at rest by our storage provider: Cloudflare R2 encrypts every object and its metadata automatically.
Access Controls
Eight roles, each a set list of what that person can do, with per-person switches for bank statements, revenue and margins, sending to your accounting system, downloads and deleting invoices, and an approval limit per person. Permissions are enforced at the API layer, not just in the UI. Every significant action is logged.
Data Retention
You choose how long we retain your original uploaded files: 7 years, 3 years, 1 year, or Permanent. Extracted data is retained for the life of your account. Automatic age-based deletion of workspace files is not running yet — your setting is recorded and will govern that sweep when it is enabled. An invoice you delete goes to Trash for 30 days, then it and its file are permanently deleted. Closing your account permanently deletes every workspace only you belong to.
Infrastructure Security
CSRF mitigation via Origin/Referer validation on all state-changing requests. Per-user rate limiting on upload endpoints. Security headers enforced on every response.
Every service that touches your data
Named by role, with the region they operate in. All core infrastructure is hosted in the United States. See our Privacy Policy for the full disclosure including what each provider does with your data.
| Provider | Role | Region |
|---|---|---|
| Azure Document Intelligence | Primary OCR / layout extraction | US |
| OpenAI (GPT-4o) | Reads and checks documents (text and page images) | US |
| Cloudflare R2 | Object storage for original uploaded files | US |
| Railway Postgres | Primary application database | US |
| Vercel | Frontend hosting and edge delivery | US |
| Valkey / Redis | In-memory cache and job queue (no invoice content) | US |
| Stripe | Payment processing | US |
| Resend | Sending and receiving email (transactional email, invoices emailed to IPP addresses, support correspondence) | US |
| Sentry | Error tracking and performance monitoring | US |
| Slack | Optional approval notifications (vendor names and invoice totals) | See Slack service terms |
| PostHog | Product analytics and session replay | US |
Authentication providers
Optional third-party sign-in. These providers authenticate your identity only — they never receive invoice content, extracted data, or account data beyond the email address they return to us.
| Provider | Role |
|---|---|
| Optional "Sign in with Google" — authenticates identity and returns a verified email. Receives no invoice or account data. | |
| Microsoft | Optional "Sign in with Microsoft" — authenticates identity and returns a verified email. Receives no invoice or account data. |
All infrastructure is US-hosted
Our primary database (Railway Postgres), object storage (Cloudflare R2), and extraction pipeline (Azure Document Intelligence and OpenAI) all operate in the United States. If you access the Service from the European Economic Area, the United Kingdom, Switzerland, or any other region outside the United States, your data will be transferred to, stored, and processed in the US in the ordinary course of providing the Service.
We don't offer a signed Data Processing Addendum (DPA) yet. Email security@invoiceparserpro.com and we'll tell you where it stands.
Where we are. Where we're going.
The controls above include their current limitations, including the retention sweep that is not yet enabled. The items below are on the roadmap but not yet in place. We will update this page when their status changes.
Questions about security?
We answer technical security questions directly. Email security@invoiceparserpro.com.
We aim to acknowledge security inquiries within one business day.
Last updated: October 8, 2026